Your AI asks.
Helios decides, and logs it.
A gateway for every model call, and agent protection: what agents can call, and who signs off.


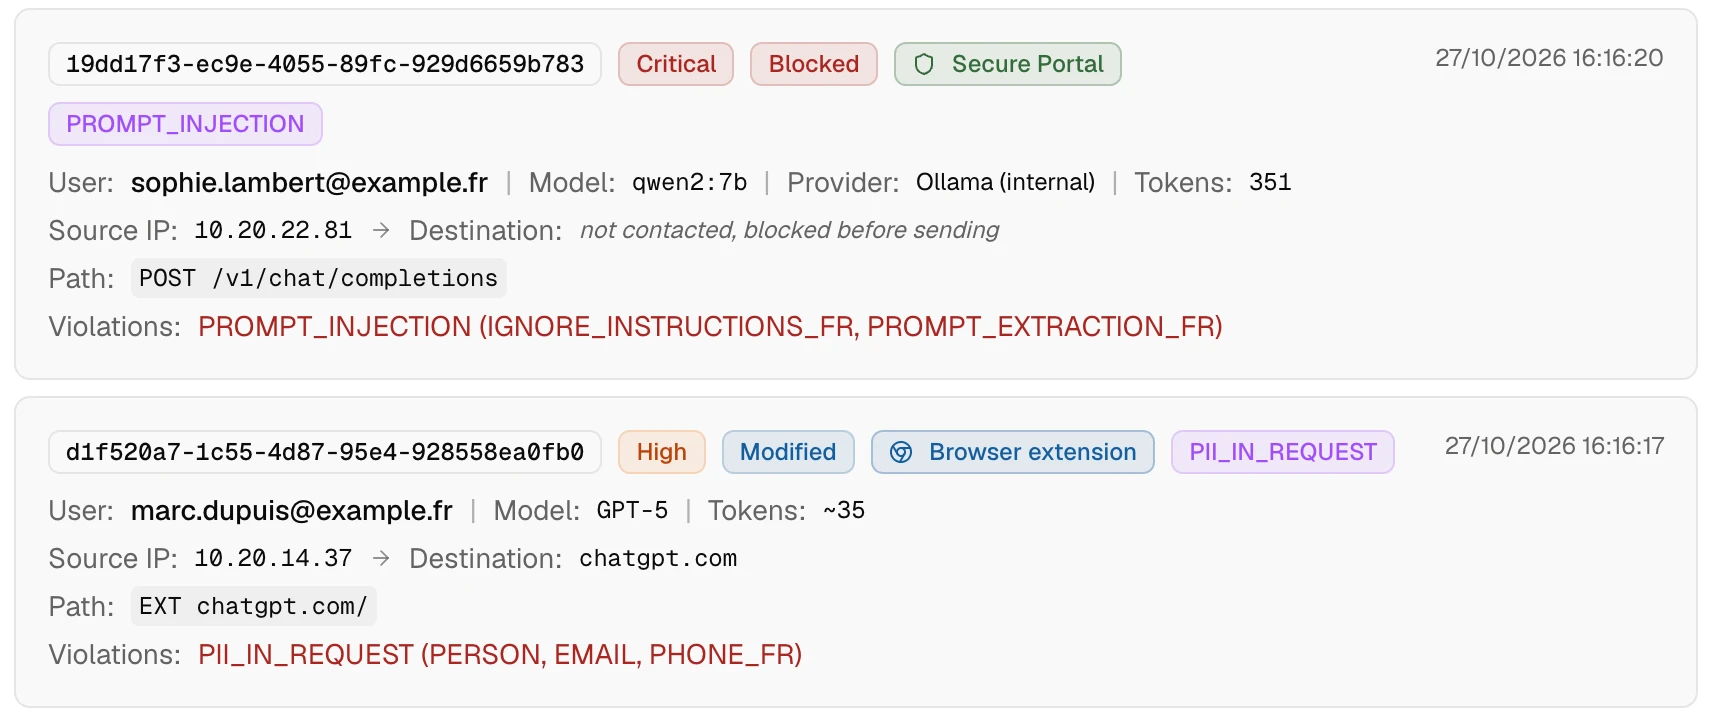
One point of passage for every model call.
Three doors, one gateway: everything in is inspected, everything out is logged.
- OpenAI-compatible APIYour applications: change the address, keep the code.
- Chrome extensionThe web AI assistants, secured in the browser.
- Secure portalAn in-house AI assistant, governed by your policies.
Change the address.
The gateway does the rest.
- Inline guardrails. PII, secrets, jailbreak, injection, on the prompt and on tool output alike.
- Cost per team. Alert at 80%, block at the ceiling, models restricted by role.
- Models scanned before deployment. Safetensors, PyTorch, GGUF, pickle: suspicious code or a malicious pickle, and the model waits for your review.
The day AI stops answering and starts acting.
An agent queries a database, sends an email, triggers a payment. Helios decides what it is allowed to do.
-
Indirect injection
A booby-trapped ticket or PDF the agent will read: the prompt is clean, the tool output is not.
Reference: OWASP LLM01, MITRE ATLAS
-
Excessive agency
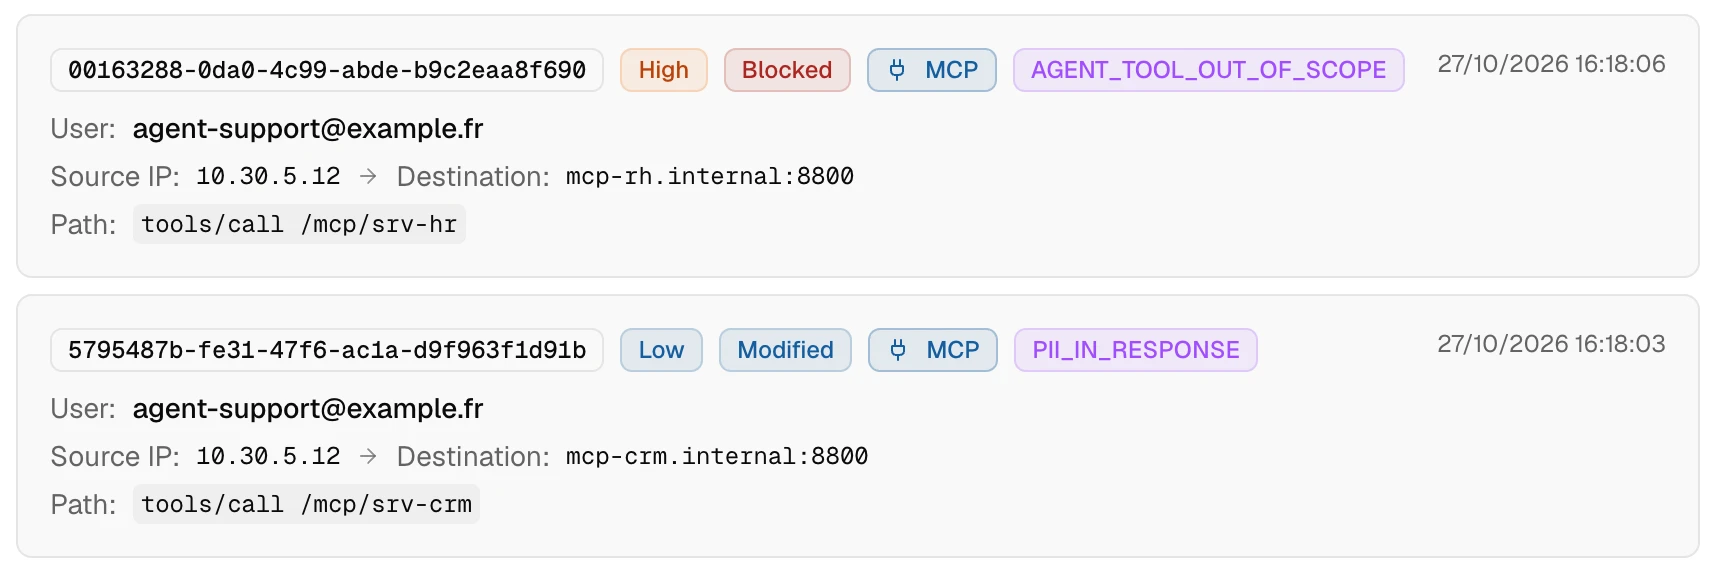
A support agent that can read the HR database: every MCP server plugged in widens its scope.
Reference: OWASP LLM06
-
Loops & drift
An agent stuck in a loop burns a quarterly budget overnight, unseen by your APM.
Reference: OWASP LLM10
Autonomy, yes.
A blank cheque, no.
- Per-agent scope. MCP tools declared, signed, revocable; short-lived secrets.blocked
- Tool output inspected. Treated as hostile input, before the agent reads it.modified
- Human sign-off. On anything irreversible, the agent prepares and a named human signs. Dual signature available.needs sign-off
- Per-run ceilings. Steps, duration, cost. Past that, an immediate halt and a SIEM alert.halted
What your architecture review board will ask.
What if the gateway goes down?
Fail-closed by default. A call the gateway can neither arbitrate nor log does not go out. Fail-open is possible per team, flagged for as long as it lasts.
One exception, not configurable: irreversible actions stay fail-closed, always.
How much latency does it add?
A number we do not publish. Three sources: policy, guardrails, the log write.
The overhead is measured on your traffic during the evaluation, and that number can go in the contract.
Who runs it, and where?
- Sovereign SaaS We operate it, in Europe, and in France for regulated scopes, audit logs included.
- Dedicated private cloud We operate an instance that is yours alone, in the region you choose.
- Your infrastructure You operate a containerised stack.
On your infrastructure, we have no access at all.
Who can read your data.
No operator access to your data, except for incident response, with your explicit approval — and that access is logged.
- Nothing comes back to us
- No product telemetry, no usage collection, no training on your prompts, in all three deployment modes.
- Append-only audit log
- Every call and every agent action, timestamped, exportable to your SIEM.
- Inference path
- Local model (vLLM, Ollama): your prompts stay in-house. Remote model: only the providers you configure receive them.
Hosted by a European cloud provider certified ISO 27001, 27017 and 27018, or installed on your premises as a self-hosted deployment. GDPR, the EU AI Act, DORA and NIS2 shaped the architecture from the first line.
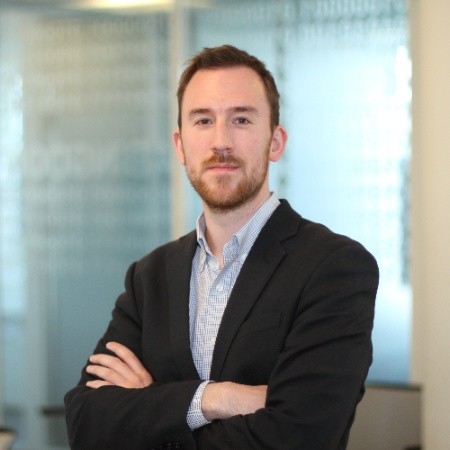
You have had this conversation before. I was on the other side of the table.
Ten years in cybersecurity presales, at the vendors already running in your SOC: Sophos, Trend Micro, VMware Carbon Black, Varonis.
Check on LinkedIn (opens in a new tab)It all starts with an evaluation.
One use case, on your real traffic, for a few weeks, with an engineer. After that, you pay for the gateway, never a percentage of your tokens.
-
Evaluation
You pick the scope; we plug Helios in and measure with you.
- Full audit log
- Latency measured on your traffic
- An engineer alongside you
-
Gateway
In production: everything that calls a model runs through it.
- Models & volumes uncapped
- SSO/SAML · RBAC · budgets
- Fail-closed configurable per scope
-
Gateway + Agents
Both pillars, for agents that write to your business systems.
- MCP control & agent identity
- Dedicated private cloud or your infrastructure
- On-call and service commitments negotiated
One use case, your traffic, a few weeks.
You leave with the latency measured on your side and an audit log your CISO can read, whether you sign or not.